AI policy, inventory and training
Your customers are asking how you use AI. Have an answer.
We inventory the AI tools your team uses, set policy and controls, train your people and map it all to NIST AI RMF and the EU AI Act. A program in place in weeks, run by the same experts who handle your SOC 2.
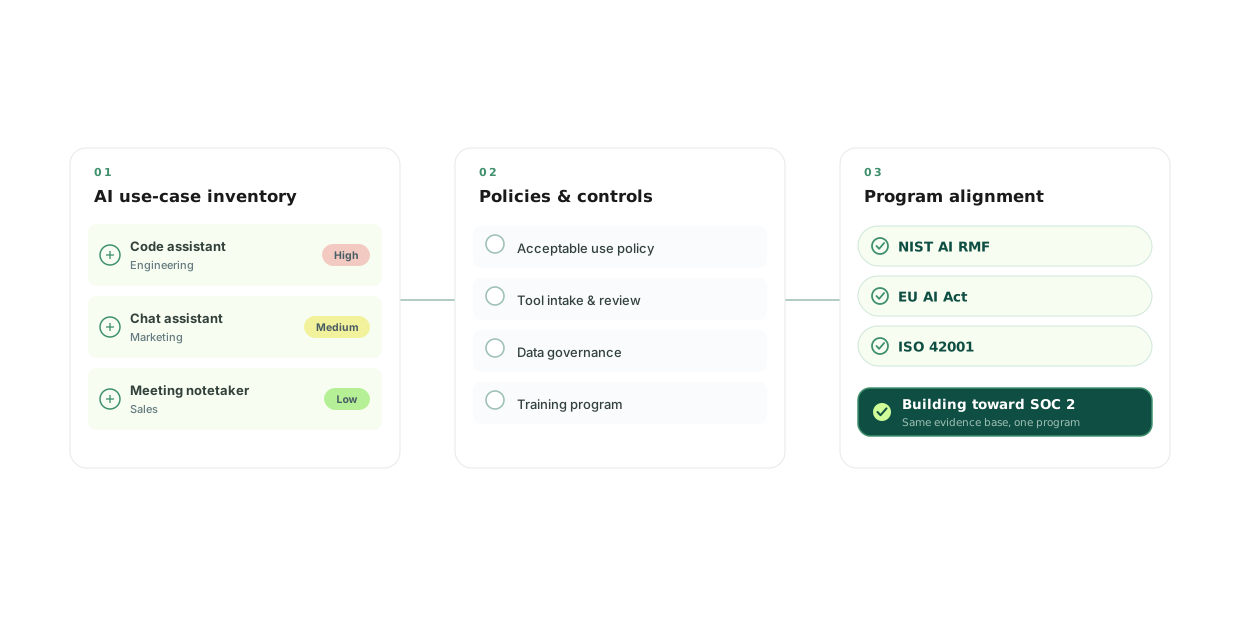
For firms whose teams are already using AI with client data: no framework, no inventory of where AI touches sensitive data, and pressure mounting from leadership and customers. We build the policies, workflows, and controls to manage AI risk. One expert-owned outcome that becomes your source of record, not a tool to figure out yourself.
Your team is already using AI with customer data. There's no list of which tools, no rules for what they can touch and no review before they're used. Then a customer's security questionnaire asks about all three.
We don't sell a framework. We build a program that holds up against them.
Your program is structured so it maps cleanly to whichever standard your buyers or regulators reference: NIST AI RMF, ISO 42001, EU AI Act, and US state AI rules.
AI Governance Program
Use-case inventory, risk classification, data governance, tool intake policy, acceptable use policy, training program. The full program, documented and defensible.
EU AI Act & NIST AI RMF Alignment
Map your program to the two frameworks your enterprise clients and regulators reference most. Demonstrate alignment without over-engineering.
AI governance is a trust problem.
|
Most AI programs fail because IT builds a tool list, Legal writes a policy and neither answers the questions customers actually ask. We run AI governance with the same team and evidence as your SOC 2 and sustainability work, so every answer matches. |
Your next customer questionnaire will ask about AI. Be ready.
Get a free AI governance assessment. We'll map what your customers will ask, what you already have and how fast we can close the gap.